Security telemetry

Logging, SIEM, and Telemetry Engineering

Build visibility that supports real investigation paths instead of noisy dashboards and incomplete logs.

When this helps

What this covers

  • Telemetry coverage mapping across cloud, identity, SaaS, endpoint, network, and applications.
  • Normalization strategy using schemas such as ECS and OCSF where they help.
  • Detection catalog design tied to MITRE ATT&CK and critical risks.
  • Retention design that balances forensic depth, query performance, and cost.
A defined starting engagement

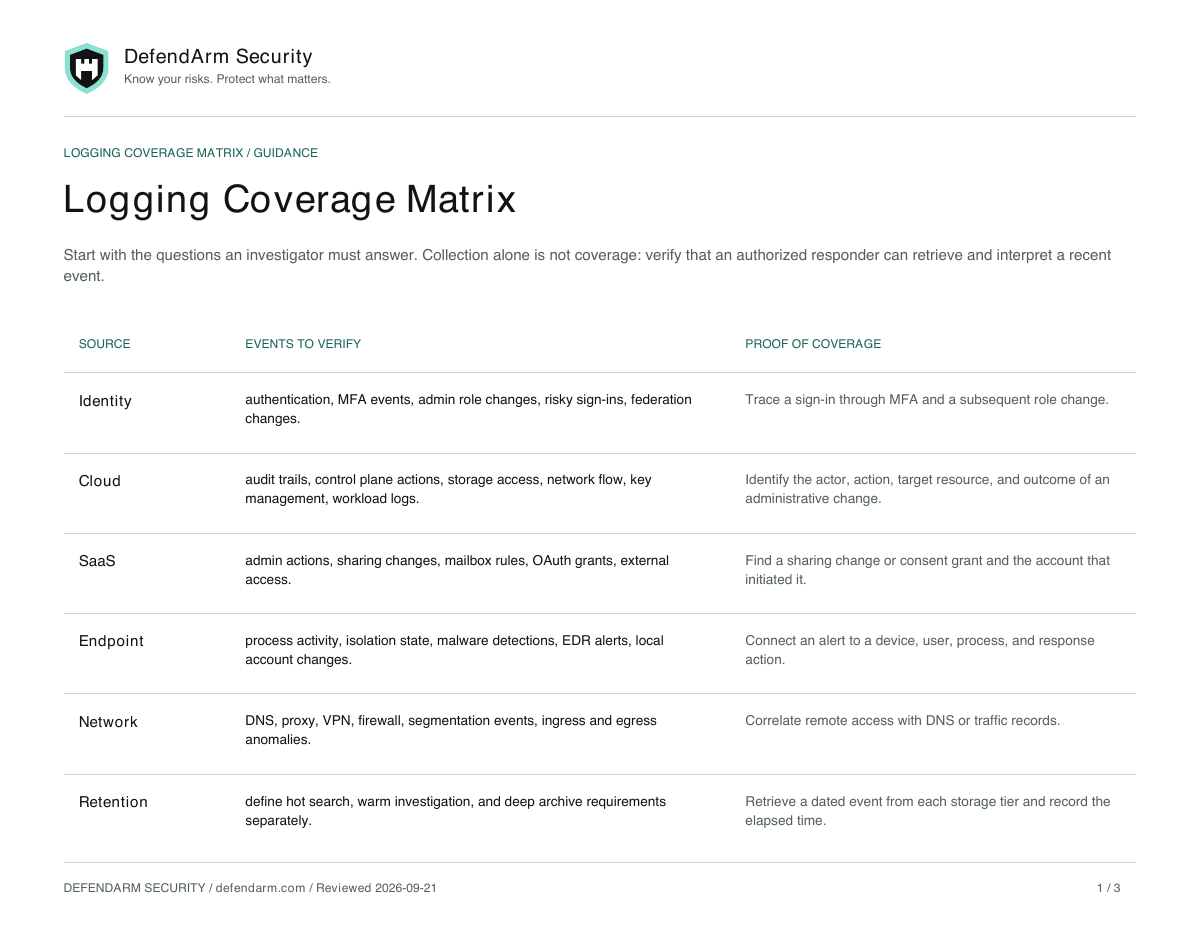
Logging coverage review

For teams that need to know whether their logs can answer incident questions before buying more storage or changing SIEM platforms.

Illustrative deliverable / not a client result
First page of Logging Coverage Matrix
Logging Coverage Matrix / first-page preview

Archive retention exists, but retrieval is untested

Get the related workbookDiscuss this engagement

Questions and answers

What access and staff time are needed?

Source inventory, approved event samples, retention settings, and supervised query access where needed. Share evidence only through an agreed channel. A logging owner plus the relevant identity, cloud, SaaS, or endpoint administrators for evidence questions and findings validation.

How is the work scheduled?

Define investigation questions, map coverage, test retrieval, and review the prioritized plan. The proposal confirms duration after source count, evidence access, and retrieval scope are known.

What is outside this engagement?

Platform licensing, full SIEM deployment, round-the-clock monitoring, incident investigation, and production migration are separate scopes.

How is the fee determined?

Source count, platform diversity, archive retrieval work, and any requested implementation support determine the quote. Collection changes and engineering work are priced separately unless included explicitly.